No AI Act ≠ No Obligations: What Australian Boards Need to Evidence on AI
Australia has no AI Act, that’s why AI governance is harder. What boards should evidence across APRA, ASIC, OAIC and accountability regimes.
Australia doesn’t have an AI Act.
That’s exactly why this is harder for boards of regulated entities.
In jurisdictions with a single, named statute, directors can point to a chapter, a risk tier, and a compliance programme built around that text. In Australia, AI obligations are real but scattered, across prudential expectations, privacy, conduct, and accountability regimes boards already live under. Plenty of organisations have a policy PDF. Far fewer can produce evidence of what AI ran, under which rule, attributed to whom.
Governance you can’t evidence isn’t governance.
This article is for directors and risk leaders who need a clear, non-legalistic view of what “good” looks like: not another principles document, but a practical evidence bar. It is not legal advice. Treat regulator references as high-level context and confirm specifics with counsel and your advisory team.
The scattered obligation surface
Australian regulated entities don’t need to wait for a dedicated AI Act to have duties. Boards already oversee technology, operational resilience, privacy, and accountability under existing frameworks. AI changes the shape of those duties; speed, opacity, non-human actors, and third-party model supply chains... more than it invents a brand-new category of “ethics theatre.”
At a high level, the surface often includes:
- Prudential and operational resilience expectations for APRA-regulated banks, insurers, and superannuation trustees, including how AI affects critical operations, cyber posture, and assurance.
- Conduct and licensee obligations where AI touches customers, advice, claims, or markets (ASIC-relevant contexts).
- Privacy, especially transparency around automated decision-making that significantly affects individuals (OAIC / Privacy Act reforms).
- Accountability regimes boards already recognise (including FAR-adjacent accountability for relevant entities). Someone must own outcomes, not “the model.”
The practical problem: each regime asks related questions in a different language. Without a single inventory and a single evidence trail, teams rebuild the same answers in four different places.
What APRA publicly signalled in 2026
In April 2026, APRA published a letter to industry on artificial intelligence after engaging with selected large banks, insurers, and superannuation trustees. The public message was blunt: adoption is moving faster than governance, risk management, and assurance.
Among the themes boards should read carefully (again: high-level, not a substitute for the letter itself):
- Boards need sufficient AI literacy to challenge management, not rely solely on vendor presentations.
- Entities need an inventory of AI tooling and use cases, with ownership across the lifecycle.
- Preventative controls matter; policy direction and after-the-fact detection alone are weak calibration to risk appetite.
- Assurance that is only point-in-time or sample-based struggles with systems that adapt, degrade, or act through agents.
- Supplier concentration and opacity (foundation models, embedded AI in platforms) complicate independent assessment.
You can read the letter on APRA’s site: APRA Letter to Industry on Artificial Intelligence (AI).
For a board, the translation is simple: interest in AI benefits is not the same as oversight of AI risk. The question is whether you can evidence strategy-aligned use, controls that actually fire, and assurance that keeps pace.
Frameworks are not evidence
Many board packs still stop at:
- We have an AI policy.
- We have a working group.
- We trained staff.
- We are “aligned” to a global framework.
None of that answers the question a sceptical director, or an auditor, should ask next:
Show me what AI is in use this month, what was blocked or allowed, and who is accountable for the outcome.
A framework is a map. Evidence is the telemetry.
| Artefact | What it proves | What it doesn’t |
|---|---|---|
| Policy PDF | Intentions | That controls ran |
| Training completion | Awareness | That sensitive data didn’t leave via an unsanctioned tool |
| Vendor SOC report | Supplier controls (partial) | Your usage, your prompts, your agents |
| Risk committee minutes | Oversight process | Completeness of inventory |
| Audit trail of AI interactions | What ran, under which rule, by whom | n/a |
Kinnatic’s position is deliberate: Evidence, not intentions. For regulated entities, the product of AI governance is not a slide, it’s an assurance-grade trail.
A board-ready evidence checklist (practical)
Use this as a discussion guide with your CISO, CRO, and AI governance owner. Adapt to your industry and specific requirements.
1. Inventory completeness
- Do we maintain an active inventory of AI tools and use cases, including shadow / unsanctioned use, or only a registry of what people remembered to declare?
- Can we distinguish sanctioned enterprise tools, embedded AI in SaaS, browser-based assistants, APIs, and agents?
2. Ownership and risk appetite
- Is there named ownership across the lifecycle (design → deploy → monitor → decommission)?
- Are AI uses mapped to risk appetite with clear escalation triggers?
3. Controls before execution
- Does policy sit between people (and agents) and the model, or only in a handbook?
- Can we block, redact, or route based on data class and use case? And prove it?
4. Assurance and auditability
- Can we produce, on demand: what ran, under which policy version, attributed to which identity?
- Is assurance continuous enough for the criticality of the use case, or only annual sampling?
5. Third parties
- Do we understand material model and platform dependencies, including concentration risk and exit credibility?
- Are contractual audit/notification expectations matched by operational visibility?
If several answers are “we think so” or “it’s in a spreadsheet,” you have a discovery and evidence gap, not a communications gap.
The false comfort of “we’re early”
Boards sometimes hear that AI governance can wait until “production” use cases mature. That framing misses how AI actually enters enterprises: through browser tabs, copilots in sanctioned suites, vendor features flipped on by default, and agents wired to tools over a weekend.
Shadow AI doesn’t wait for your AI Act.
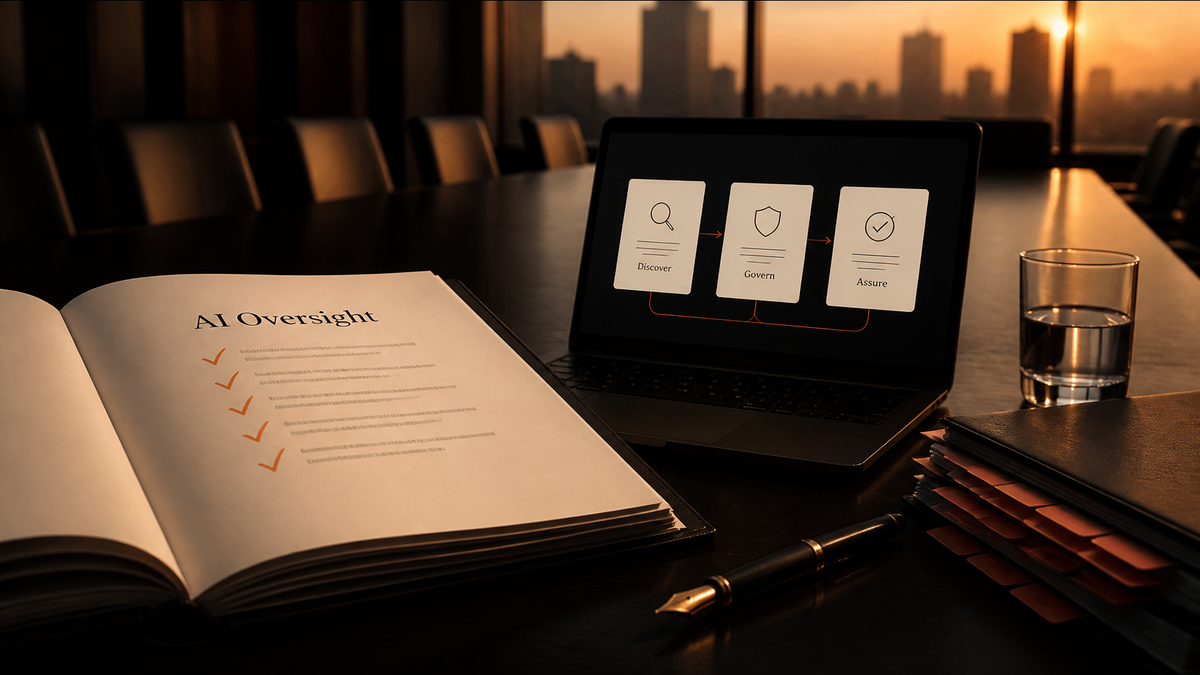
The organisations that stay defensible treat discovery as the door, governance as the control plane, and assurance as the output directors and auditors can inspect. That sequence, Discover → Govern → Assure, is how Kinnatic is built for regulated entities.
What to do this quarter
- Ask for an inventory you didn’t write yourself, one that surfaces unsanctioned tools, not only approved pilots.
- Pick one high-sensitivity workflow and demand pre-execution policy plus a reconstructable trail.
- Schedule a board education session that includes failure modes (data leakage, agent overreach, supplier opacity), not only productivity demos.
- Align internal audit early; don’t discover your evidence gap in the week before a thematic review.
Start with visibility
If you can’t see AI usage, you can’t govern it, and you can’t assure it.
Kinnatic is an AI governance platform for regulated enterprises. See which AI tools show up in your organisation, then decide how to put enforceable policy in front of them and keep an audit trail.
Built for teams who need evidence, not intentions.